So you’ve been hearing about Kimi AI. Maybe a friend showed you how fast it handles long PDFs, or you saw a thread on Reddit raving about its 2M-token context window. And now you’re wondering the one thing that really matters before you paste in your work notes, tax documents, or half-written novel: is this thing actually safe?
If you ask, is Kimi AI safe to use? The answer isn’t easy, maybe yes or no. It depends on what you’re using it for, what you’re typing into it, and honestly, how paranoid you are about where your data ends up. I’ve spent a fair amount of time poking around Kimi, reading the privacy policy (yes, the whole thing), and digging through independent security reports. What I found is more nuanced than the loud takes on either side suggest.
Let me walk you through it like a normal human would no corporate handwaving, no doomsday fearmongering. Just the facts, a few opinions, and some practical advice you can actually use.
What Is Kimi AI?
Kimi is an AI chatbot built by Moonshot AI, a Beijing-based startup that launched in 2023 and is backed by Alibaba. Think of it as China’s answer to ChatGPT and Claude, except with a few twists that actually make it stand out.
Its headline feature is a monstrously long context window (up to 2 million tokens in the latest K2.6 release), which means you can dump an entire novel, a massive codebase, or a stack of legal contracts into it and ask questions. It’s also priced aggressively cheap — the API costs roughly one-eighth of what top-tier U.S. models charge. That pricing alone is why you’re seeing developers, students, and small businesses quietly switching over (IAPS research).
But low price and long context come with trade-offs. And the biggest trade-off, unsurprisingly, is trust.
The Short Answer: Is Kimi AI Safe?
Let me be upfront. For casual, non-sensitive tasks, brainstorming blog ideas, summarizing a boring PDF, and helping your kid with homework. Kimi is generally safe in the same way most AI chatbots are “safe.” You’re not going to get malware from typing a prompt.
But here’s where it gets interesting. There are three different kinds of “safe” that people usually mean when they ask this question, and Kimi performs very differently on each one:
- Operational safety — Will it work reliably without crashing or doing weird things? Mostly yes.
- Content safety — Does it refuse to generate harmful content? Mixed. Independent red-team tests found real gaps.
- Data privacy — Is your information protected, and who can legally access it? This is where things get complicated.
Most articles online conflate these three, which is why you’ll see wildly different takes. Let’s unpack each one properly.
The Privacy Question Nobody Wants to Explain Clearly
Okay, let’s talk about the elephant in the room. Kimi is made by a Chinese company. That fact alone triggers a lot of reflexive reactions, some fair and some not. I’m going to try to keep it grounded.
Where your data actually goes
When you use kimi.com, your conversations, prompts, uploaded files, and generated outputs are sent to Moonshot’s servers. According to Moonshot’s own privacy policy, they collect this content and may use it to “provide, maintain, develop, and improve the services” and to “comply with applicable law.”
That last phrase is the one that makes security researchers nervous. Here’s why.
Although the consumer-facing privacy policy lists the service provider as Moonshot AI Pte. Ltd., a Singapore-incorporated entity, the parent company is based in Beijing. A detailed analysis by the Institute for AI Policy and Strategy pointed out that the privacy policy never actually mentions China, Beijing, or even Singapore by name, which creates a somewhat misleading impression of where your data might ultimately sit.
Under Article 7 of China’s National Intelligence Law, Chinese authorities have broad legal power to compel Chinese companies (and their subsidiaries) to hand over data. That’s not a conspiracy theory — it’s the actual text of the law. So the honest answer is: if Chinese regulators wanted access to your Kimi conversations, there’s a plausible legal pathway for them to get it.
Is that likely to matter if you’re asking Kimi to rewrite your cover letter? Almost certainly not. Is it a concern if you’re a defense contractor, a journalist working on sensitive stories, or an enterprise handling regulated customer data? Yeah, it is.
How Kimi compares on privacy
Let’s be honest, no major AI chatbot is a privacy paradise. Here’s a rough comparison so you can see where Kimi actually lands:
| Concern | Kimi AI | ChatGPT | Claude | Gemini |
|---|---|---|---|---|
| Stores prompts by default | Yes | Yes | Yes | Yes |
| Uses your data for training (default) | Yes, unless opted out | Yes (free tier) | No | Yes (free tier) |
| Primary jurisdiction | China / Singapore | United States | United States | United States |
| Subject to China’s National Intelligence Law | Yes (via parent co.) | No | No | No |
| Offers enterprise/no-retention tier | Limited | Yes | Yes | Yes |
| Open weights available | Yes (K2 series) | No | No | No |
The open-weights angle is actually a big deal, and it’s something most people miss. Because Kimi K2 is open-source, you can technically run it on your own hardware — no data leaves your machine, no Chinese servers involved. That’s a meaningful privacy escape hatch if you have the technical chops.
What Independent Security Researchers Actually Found
Here’s where things get interesting and a little uncomfortable.
A red-team security firm called SplxAI ran a pretty brutal evaluation of Kimi K2 back when it launched. Out of the box, with no system prompt or safety guardrails, the model scored a jaw-dropping 1.55% on security and 4.47% on safety (SplxAI red-team report). For comparison, Claude scored 34.63% and 39.72% on the same test with zero guardrails.
What does that mean in plain English? The raw model could be easily tricked into producing things like:
- Step-by-step instructions for explosives
- Harassment and profanity aimed at users
- Social engineering suggestions (like asking users invasive personal questions under false pretense)
Now, and this is important, those results are for the raw open-weights model without any safety layer. When SplxAI applied their hardened prompt system, safety scores jumped to around 82%. The consumer-facing kimi.com website presumably has its own guardrails that most users never see.
But here’s the honest takeaway: Kimi’s baseline safety training is measurably weaker than what you’d get from Anthropic or OpenAI. Whether that matters depends on whether you’re the person using it or the person whose data is being processed by it. If you’re deploying Kimi in a customer-facing product, you’d better be layering your own safety on top. That’s not optional.
What Most People Get Wrong About “Chinese AI”
Here’s where I’m going to push back on some of the louder takes you’ll see online.
A lot of commentary treats “Chinese AI = automatic spyware.” That’s lazy thinking. Moonshot isn’t scraping your hard drive or watching your webcam. It’s a chatbot. The actual risk profile is much more specific: your text inputs and uploaded files may be retained, may be used for model training, and may be legally accessible to Chinese authorities if they ever ask.
That’s a real risk for some people. For most people — students, casual users, folks asking for recipe ideas it’s a theoretical one. The key is knowing which category you fall into before you decide.
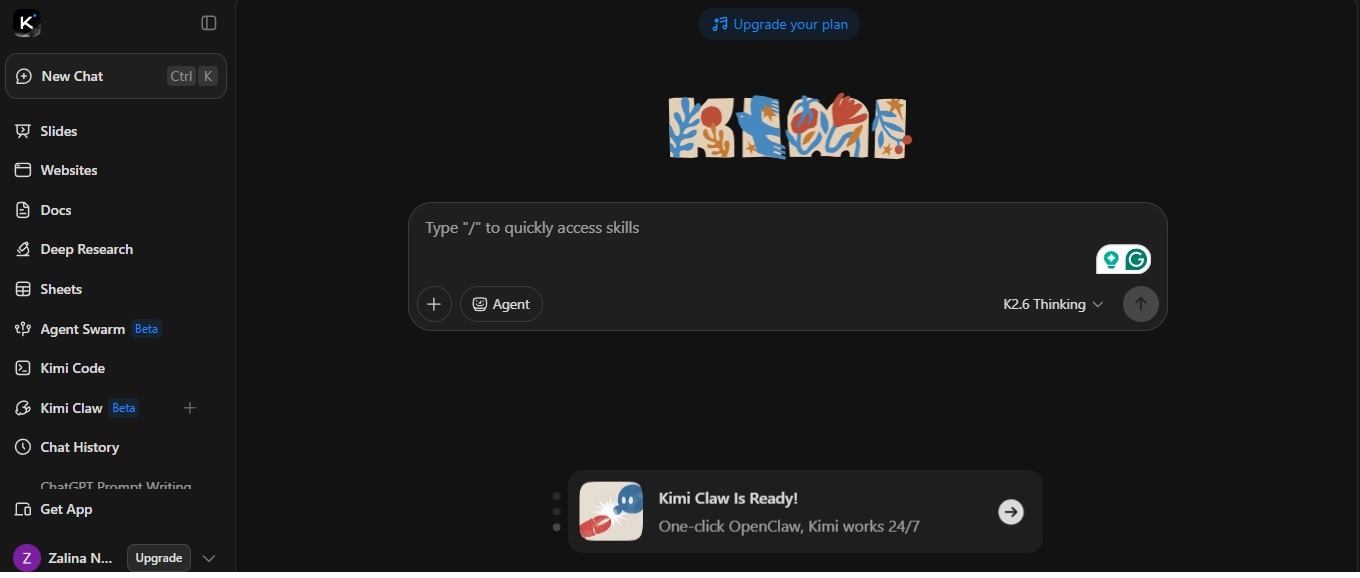
On the flip side, the “it’s fine, relax” crowd often ignores the actual technical concerns that independent researchers have flagged, including the weaker safety training and, more recently, the Kimi Claw “always-on” agent feature, which lets the AI observe and act across your digital life. That’s a genuinely new category of risk that deserves a sober second look, not a dismissive wave.
Real-Life Scenarios: Should You Use Kimi?
Let me make this practical. Here’s how I’d think about it for different types of users.
The casual user or student
If you’re using Kimi to summarize lecture notes, brainstorm essay topics, or help with language practice, you’re fine. Don’t upload your Social Security number or medical records, but honestly, you shouldn’t be doing that with any AI chatbot anyway. Kimi’s long-context feature is genuinely excellent for academic work.
The content creator or freelancer
Here’s where I’d start being more thoughtful. If your unpublished work goes into a Kimi prompt, understand that under the default privacy terms, that content could be retained and potentially used in some form. For a rough draft of a blog post, no big deal. For an original screenplay you’re about to shop around? I’d either use a model with stronger privacy guarantees or run Kimi’s open-weights version locally.
The privacy-conscious professional
Avoid putting anything sensitive — client data, legal documents, confidential strategy — into the consumer-facing Kimi app. If you love the model itself, look into self-hosting K2 through a provider that offers a zero-retention policy. Some API resellers explicitly don’t train on inputs; read those terms carefully.
The enterprise user or developer
Do not default to kimi.com for production work without a proper security assessment. Harmonic Security’s data shows that roughly 1 in 12 employees at some companies have already used Chinese AI tools without telling their security team, and Kimi is leading that pack (Harmonic Security). That’s a compliance nightmare waiting to happen. If you want Kimi’s capabilities, run the open-weights version behind your own infrastructure, or use a vetted U.S.-based inference provider.
Common Mistakes People Make With Kimi (and How to Avoid Them)
From talking to people and reading through forum discussions, these are the mistakes that pop up over and over.
Assuming “free” means “no cost at all.” There’s always a cost. With free-tier AI services, the cost is often your data being used to improve the model. Read the opt-out options, even if you have to click through three menus to find them.
Uploading entire folders without thinking. Kimi’s massive context window is a feature, but it’s also a trap. People love dumping whole project folders into the chat. Stop and ask yourself: Would I email this content to a stranger? If no, don’t paste it.
Treating it like a doctor, therapist, or lawyer. This applies to all AI, but it’s worth repeating. Kimi isn’t bound by confidentiality rules. Your prompts aren’t privileged communication. Keep truly personal stuff out of it.
Ignoring the “Bring Your Own Claw” warning. If you’re experimenting with Kimi’s agent features — the ones that let AI act across your apps and files — go slowly. MITRE’s ATLAS investigation documented real vulnerabilities in this ecosystem, including prompt injection and supply-chain attacks via third-party “skills”. This is bleeding-edge stuff and it’s not stable yet.
Using it for anything work-related without checking your company policy. Some companies, like Meta and others, have already restricted or banned OpenClaw-based tools on corporate devices. You don’t want to find out your firm’s policy the hard way.
Practical Tips: What Actually Works
Okay, let’s shift to the constructive side. If you’ve decided Kimi fits your use case, here’s how to use it without shooting yourself in the foot.
Turn off data-sharing settings the first time you log in. It’s buried a few menus deep, but Moonshot does offer options to limit how your data is used for training. Take five minutes. Do it once.
Use a throwaway email for signup if you’re testing it out. There’s no law that says you have to give Kimi your primary work address.
Redact before you paste. Before dumping a document into Kimi, do a quick find-and-replace on anything sensitive — names, addresses, account numbers, client info. Takes thirty seconds, saves a lot of headaches.
Compartmentalize your use cases. Use Kimi for the thing it’s genuinely great at (long documents, coding, multilingual tasks), and use a more privacy-focused option for the sensitive stuff. You don’t have to marry one AI. Most power users juggle three or four.
If you’re technical, run it locally. Kimi K2’s open weights mean you can spin up your own instance using llama.cpp, vLLM, or a hosted solution like Together AI, Fireworks, or OpenRouter. Check the terms — some providers explicitly don’t log or train on your data. That’s the best-of-both-worlds move.
Watch for updates. Moonshot has been iterating fast. Safety scores, features, and policies change. What’s true today might be different in six months. Don’t trust a Reddit thread from 2024.
Where Kimi Actually Shines
I don’t want to make this article feel like a hit piece, because honestly, Kimi does a lot of things genuinely well. Its long-context performance is arguably the best in the business right now — I’ve watched it digest entire 400-page technical manuals and answer specific questions with eerie accuracy. For students doing literature reviews, researchers parsing datasets, or developers working with large codebases, that capability is no joke.
It also handles Chinese, Japanese, and Korean language tasks noticeably better than most Western models. If you’re working in those languages, the difference is obvious within about ten prompts.
And the price-to-performance ratio is, frankly, unbeatable at the moment. That’s why so many developers are flocking to it despite the concerns. The math on API costs alone can cut project budgets by 80% or more.
So… Should You Use Kimi or Not?
Here’s my honest take, after all that.
Kimi AI is safe enough for most everyday use, as long as you don’t feed it sensitive personal, financial, or confidential business information. It’s a capable, well-built tool made by a serious company that happens to be subject to a different legal system than you’re probably used to. That last part is a real consideration, not a dealbreaker, unless your specific situation makes it one.
If you’re a casual user, the main things to watch are the same boring things you should watch with every AI: don’t overshare, review your privacy settings, don’t use it for anything you’d be mortified to see leaked.
If you’re handling sensitive data, don’t use the consumer app. Use the open-weights model through a trusted provider, or stick with a Western option that has clearer data-handling guarantees.
And if you’re somewhere in the middle — which is most of us — the answer is use it thoughtfully, not blindly. Know what you’re typing in. Know where it’s going. Keep the useful parts, skip the parts you’re not comfortable with.
That’s the grown-up version of the answer. The loud takes online will tell you it’s either perfectly fine or basically spyware. The reality, as usual, is more interesting and more manageable than either extreme.
Just don’t paste your passport scans in there. Seriously. You’d be surprised how many people do.
You May Also Like
 AI Models
Which Claude Model Is the Best Right Now? An Honest 2026 Breakdown
 AI Models
Is DeepSeek Accurate? An Honest, Practical Answer
 AI Models
Llama 4 Scout vs Llama 4 Maverick: Which One Actually Fits Your Workflow?
 AI for Coding
The Best AI Models for Developers in 2026: An Honest, Hands-On Look at What Actually Works
 AI Models
GPT-5.5 vs Claude Opus 4.7 vs Gemini 3.1 Pro: Real Benchmark Results Compared
 AI Models
